
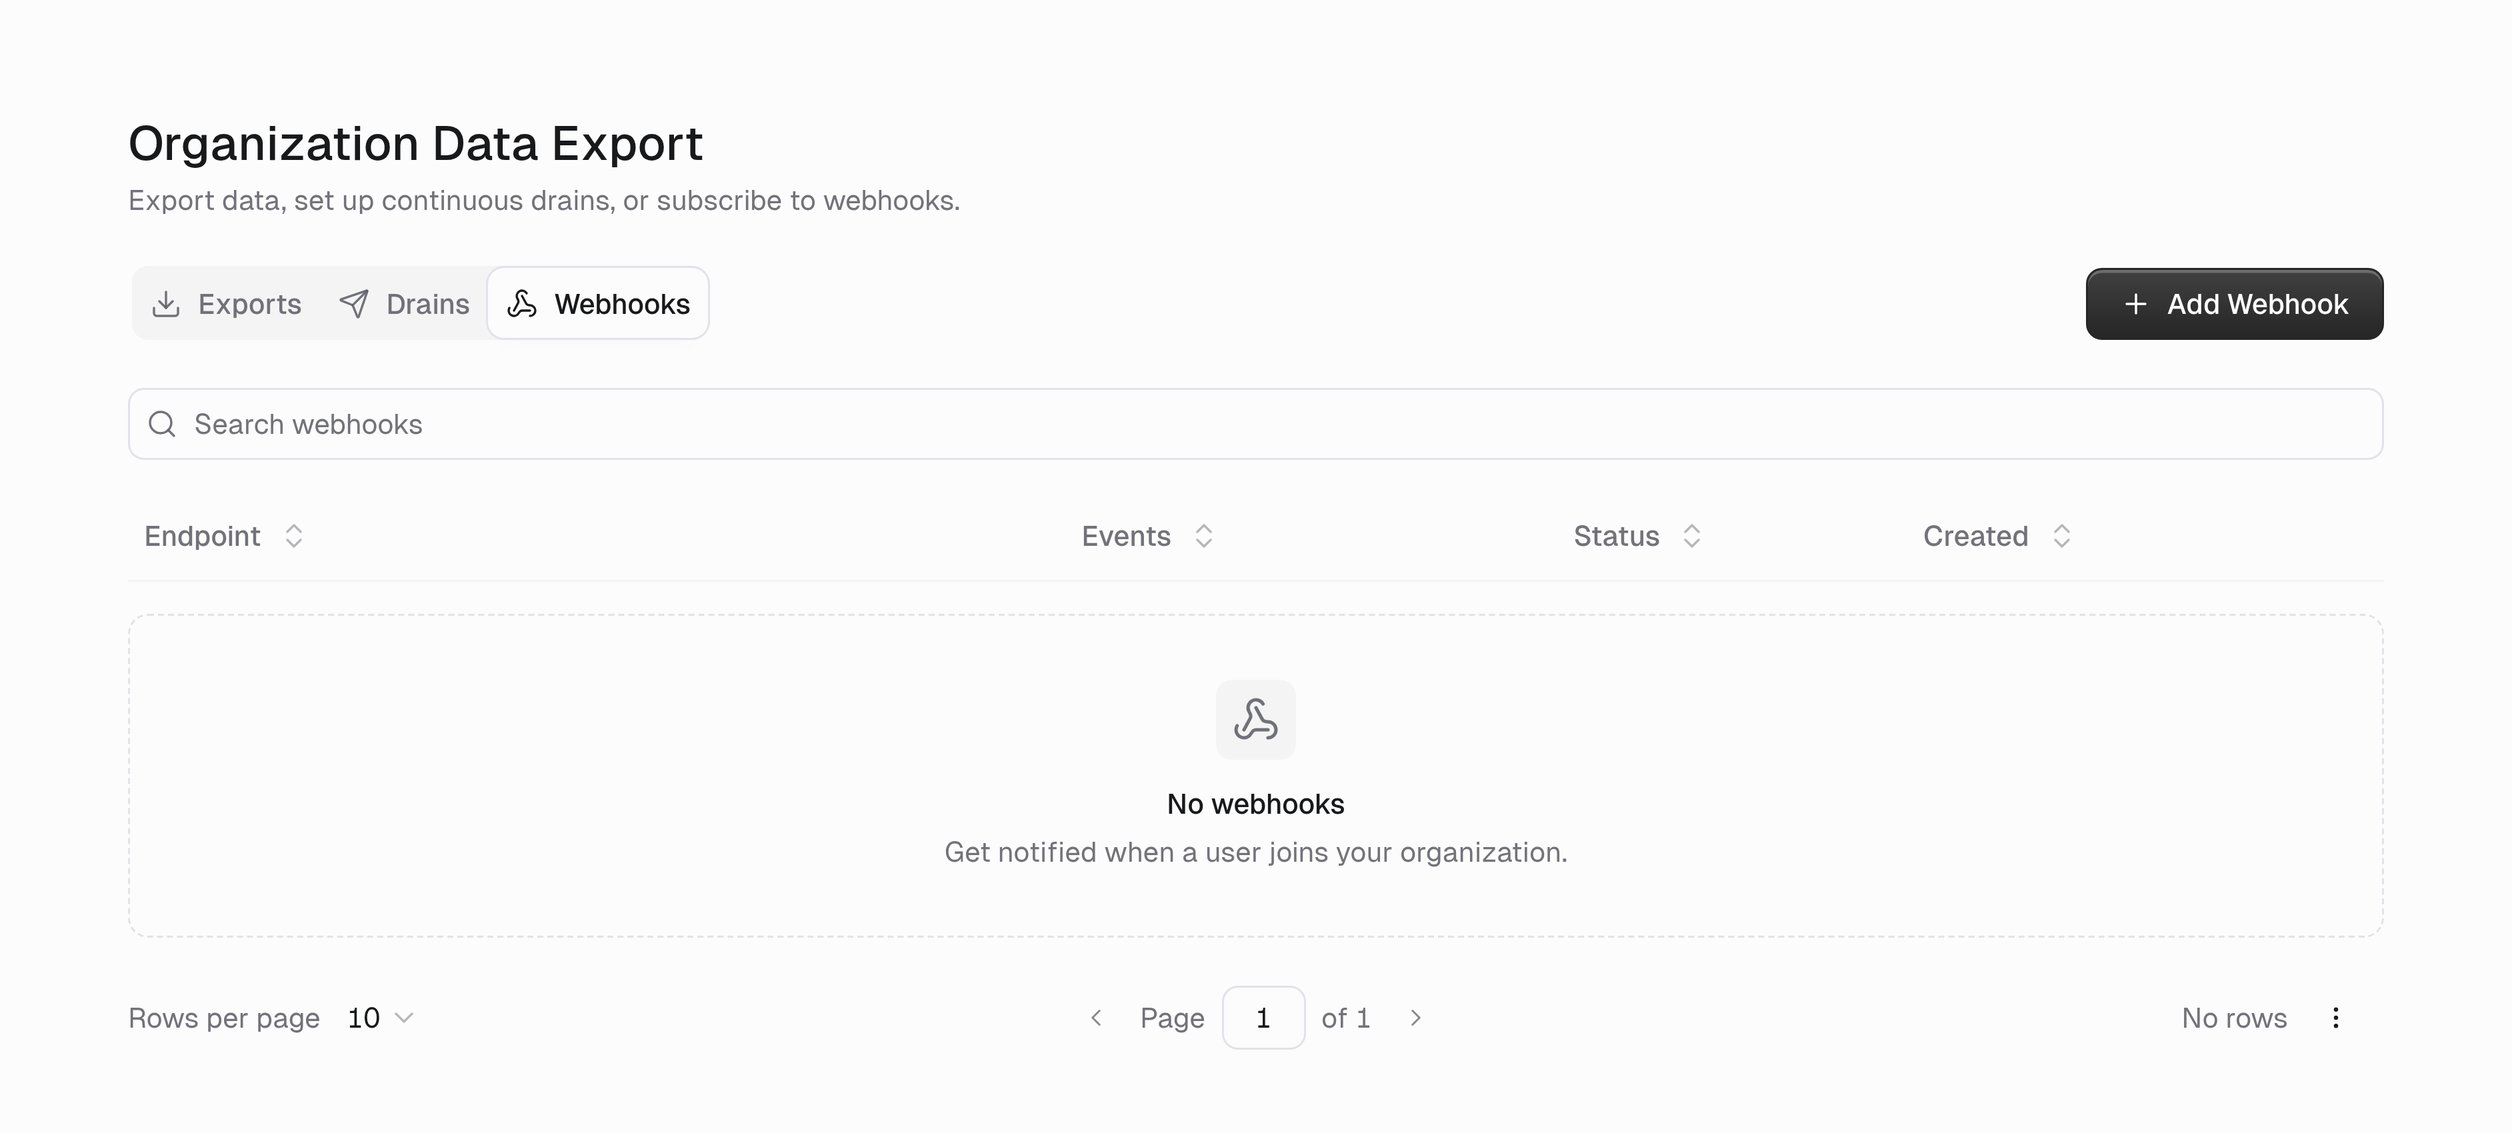
Add a webhook
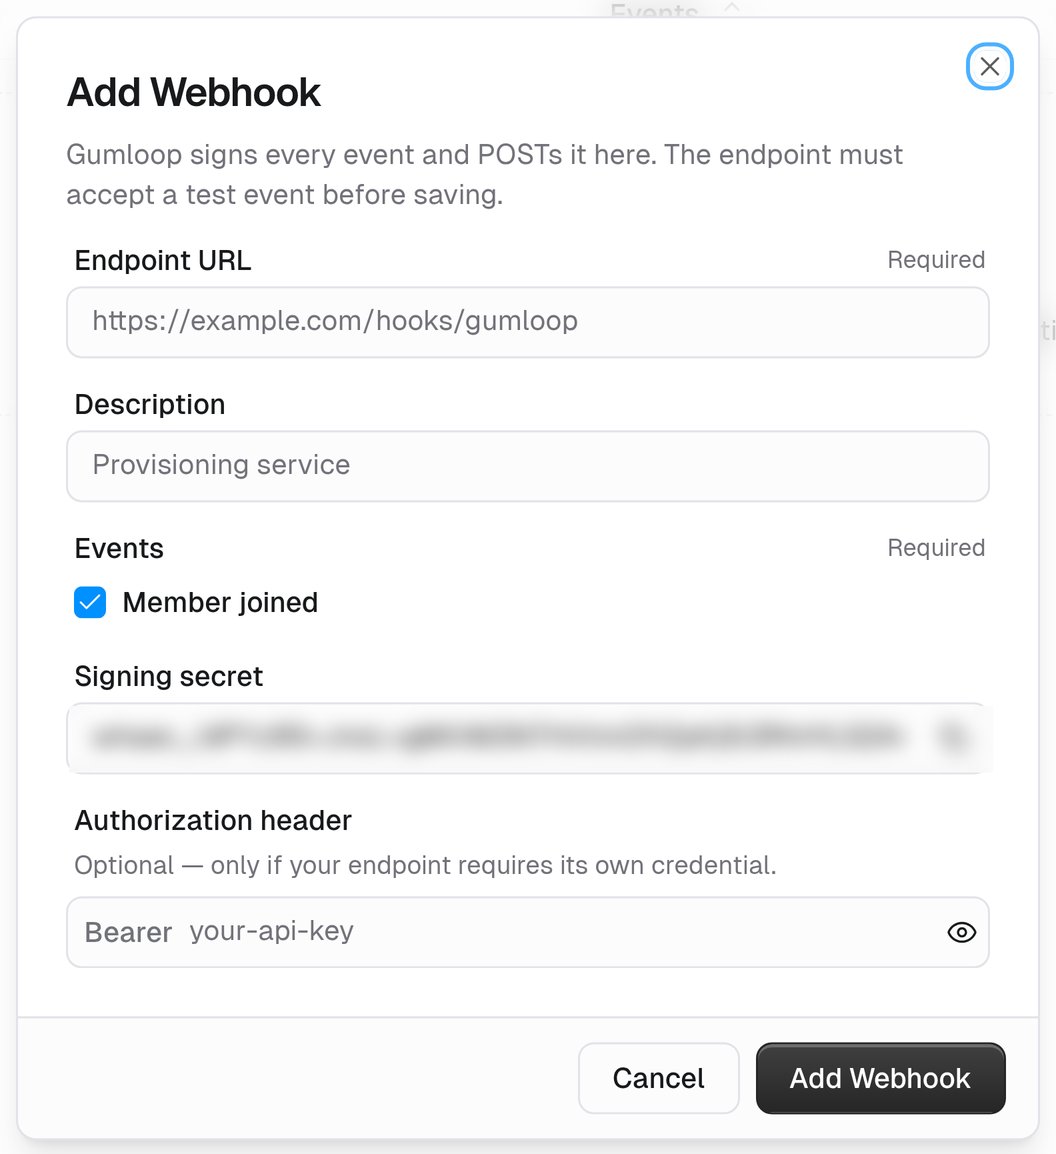
1
Enter the endpoint URL
Must be HTTPS. This is where Gumloop POSTs each event. The URL must be public, must not embed credentials, and must accept a test event with a
2xx response.2
Describe it (optional)
A note for your teammates, such as Posts to our internal provisioning service.
3
Pick at least one event
Today that is Member joined (
organization.member.joined). It reports a newly established organization membership, including accepted invitations, domain-based enrollment, and SCIM provisioning. Sending an invitation alone does not trigger it, and adding roles to an existing member does not trigger a second joined event.4
Copy the signing secret
Gumloop generates a secret starting with
whsec_. Copy it before saving or closing the dialog. It is shown during creation and replacement, but is not available in the Edit dialog afterward. If you lose it, use Replace credentials to generate a new one.5
Add an authorization header (optional)
Only use this field if your endpoint requires a bearer token. Enter the token alone, without
Bearer . Gumloop adds the prefix and sends Authorization: Bearer <your-token> on each delivery.6
Save
Gumloop sends a test event (
webhook.ping) first and only saves the webhook if your endpoint accepts it. If saving fails, check the validation message as well as endpoint reachability and the test response.What a delivery looks like
Each delivery is an HTTPPOST with a JSON body and these headers:
Make your receiver idempotent: record successfully handled event IDs and do not repeat their side effects when the same event is delivered again. A retry retains the event ID and body, but its
webhook-timestamp and signature are generated for that attempt.
Each JSON body contains:
id: the event ID, matchingwebhook-id.type:organization.member.joined, orwebhook.pingfor a test.timestamp: when the event envelope was created, as an ISO 8601 UTC timestamp.api_version: currently2026-09-10.data: the event-specific payload.
organization.member.joined, data contains:
organization:idandname.user:id,email,first_name, andlast_name.membership:join_method,roles, andprojects, where each project hasidandname.actor: an optional object containing the acting user’semail.
null when unavailable. projects can be an empty array, and actor is omitted when no acting user can be resolved.
A webhook.ping uses the same envelope, with data: {"organization": {"id": "<organization-id>"}}. Your receiver must accept this test event as well as member-joined events.
Return any 2xx status as soon as you have accepted the payload. Do the slow work asynchronously.
Verify the signature
Gumloop follows the Standard Webhooks scheme. Remove thewhsec_ prefix from your signing secret and base64-decode the remaining value to obtain the HMAC key bytes. Compute HMAC-SHA256 over <webhook-id>.<webhook-timestamp>.<raw request body>, base64-encode the digest, and compare it in constant time with the v1 signature in webhook-signature.
Python
Delivery failures and retries
Gumloop uses a 10-second HTTP timeout and does not follow redirects. For queued event deliveries, a network error or non-2xx response normally triggers up to three retries, after delays of 30, 120, and 480 seconds — up to four attempts including the initial request.
410 Gone is permanent: Gumloop marks the delivery failed and changes the endpoint to Error immediately. An endpoint also enters Error after 10 consecutive failed attempts. An endpoint that is Paused or Error does not receive queued deliveries.
After fixing the receiver, use Resume to reactivate the endpoint. Resuming does not replay deliveries already marked failed.
The test performed while creating a webhook or changing its destination or credentials must succeed before the change is saved. These preflight tests are separate from queued-event retries.
Manage a webhook
Troubleshooting
Gumloop will not save my webhook
Gumloop will not save my webhook
Check the validation message as well as endpoint reachability and the test response. The URL must be public HTTPS, must not embed credentials, and the endpoint must accept the test event with a
2xx response. If your endpoint sits behind an allowlist, see Static Egress IPs.Signature verification fails
Signature verification fails
Decode the secret after the
whsec_ prefix. Verify against the raw bytes you received, include the webhook-id and webhook-timestamp in the signed string, and compare the v1 signature in constant time.I need a different event
I need a different event
Only the events listed in the Add Webhook dialog are available. For broader data, use Usage Data Export exports or drains.
Related
Usage Data Export
One-time exports and continuous drains.
Audit Logging
A full record of activity in your organization.